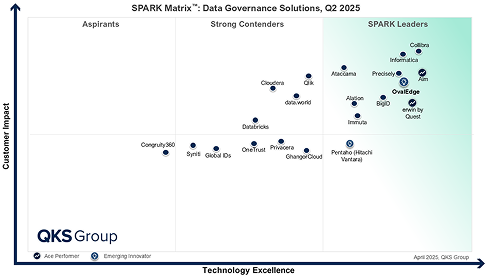
How quickly can you tell an auditor where every copy of a customer's personal data lives right now? For most compliance teams, the honest answer is "not quickly enough." That gap is exactly what GDPR data discovery software is designed to close.
A capable platform continuously locates personal data across every system in scope and keeps the inventory current without manual effort, which means the audit evidence it produces is always tied to real lineage and a defensible lawful basis. Your team stops chasing copies of data and starts managing them with confidence.
This guide compares the nine tools compliance and governance teams shortlist most often in 2026. Every section is built around one question: does this tool actually fit the way your team works.
What is GDPR data discovery software?
GDPR data discovery software identifies, classifies, and maps personal data specifically for GDPR compliance workflows. It ties data visibility directly to the obligations regulators audit against:
-
Article 30 records of processing activities
-
DSAR fulfillment within statutory windows
-
Right-to-erasure workflows with proof of deletion
-
Breach reporting with defensible scope
Unlike generic discovery, every finding is delivered with regulatory context and audit-ready evidence attached.
Generic data discovery vs. GDPR data discovery
|
Capability |
Basic data discovery |
GDPR data discovery |
|
Classification |
Generic PII patterns |
GDPR-defined personal and special category data |
|
Regulatory mapping |
Limited or none |
Article 30 documentation and audit-ready reporting |
|
Risk visibility |
Asset inventory |
Exposure scoring based on compliance impact |
|
Rights workflows |
Rarely included |
DSAR search, retrieval, deletion, and audit tracking |
|
Evidence generation |
Metadata reporting |
Defensible documentation for regulator inquiries |
Regulators expect evidence of how personal data is known and managed, not just proof that a scan ran. Manual mapping cannot keep up:
-
SaaS sprawl: Business teams adopt new tools faster than privacy teams can review them.
-
Uncontrolled copies: Exports and shared drives spread personal data into places the original map never captured.
-
Silent cross-border transfers: New vendor integrations quietly move data across jurisdictions without a policy change.
Automation keeps inventories current, protects the one-month DSAR deadline, and now extends to AI pipelines under the 2026 EU Digital Omnibus, which amends both the GDPR and the EU AI Act to cover personal data used in AI training and automated decision-making.
OvalEdge Expert Opinion: The Digital Omnibus does not create new work for governance teams. It elevates the work they have already done. The catalog, lineage, and ownership context that made personal data trustworthy for humans is now the same context that makes AI systems auditable to a regulator.
What personal data GDPR discovery tools must detect
Effective data classification software classifies personal data against GDPR definitions, not just generic PII patterns. Any tool on your shortlist should cover:
-
Direct identifiers: name, email, phone, national ID, and other fields that identify a person directly.
-
Indirect identifiers: IP address, device ID, cookie ID, and other online signals that identify a person when combined with other data.
-
Special category data: health, biometric, genetic, racial or ethnic origin, religious or political beliefs, and other sensitive categories under Article 9.
-
Processing metadata: consent status, retention rules, and lawful basis for processing.
9 Best GDPR data discovery tools in 2026
A capable GDPR data discovery tool turns raw data visibility into audit-ready compliance evidence. It links every regulatory obligation to real proof rather than a manual paper trail. The nine platforms below all clear that bar, and each one fits a different type of buyer.
OvalEdge is placed first because our evaluation is built on a governance-led lens with lineage-backed evidence as the tie-breaker. Every other tool is scored against the same criteria, and each section names our own trade-offs alongside the others.
Best GDPR Data Discovery Tools at a Glance:
|
Tool |
Best fit for |
Distinctive strength |
AI + special data |
Deployment |
Pricing Model |
|
OvalEdge |
Governance teams needing lineage-backed GDPR evidence |
Article 30 records tied to live lineage |
Article 9 detection with AI pipeline lineage |
Cloud, on-premise, air-gapped |
Custom; based on connectors, capabilities, and author users |
|
BigID |
Large enterprises with extensive data estates |
Personal data classification at petabyte scale |
Article 9 classification with AI data mapping |
Cloud, on-premise |
Custom; based on sources, connectors, deployment, and support |
|
IBM Guardium |
Regulated industries with legacy databases |
Database activity monitoring with GDPR discovery |
Special-category monitoring; limited native AI coverage |
Cloud, on-premise |
Custom; based on configuration and selected offerings |
|
OneTrust |
DPO-led programs consolidating privacy workflows |
Full privacy suite with consent management |
Separate AI governance module |
Cloud |
Custom; based on users and privacy asset inventory |
|
Securiti |
Privacy teams automating DSAR and erasure |
End-to-end privacy workflow automation |
Native Article 9 detection and AI inventory |
Cloud |
Personalized pricing |
|
MineOS |
Mid-market teams managing SaaS sprawl |
SaaS-first discovery and mapping |
Article 9 and shadow AI discovery |
Cloud |
$10,000/year for DSR handling |
|
Strac |
SaaS-heavy teams needing real-time redaction |
Browser-level DLP and remediation |
Real-time sensitive-data redaction |
Cloud |
Custom; based on coverage, integrations, data volume, and headcount |
|
Varonis |
Teams securing unstructured data |
File discovery with access governance |
Article 9 file detection; limited AI coverage |
Cloud, on-premise |
User-based licensing; 30-day unlimited trial |
|
Microsoft Purview |
Microsoft-native organizations |
Native Microsoft 365 and Azure coverage |
Special-category classifiers with Copilot governance |
Microsoft Cloud |
Microsoft 365 E5: $60/user/month, paid annually |
1. OvalEdge
Disclosure: OvalEdge is the publisher of this comparison. We've evaluated it by the same criteria as every other tool on this list.
Best for: Data governance and catalog teams that need lineage-backed GDPR audit evidence.
OvalEdge supports organizations that manage GDPR within a broader data governance program. Its Data Privacy & Compliance solution discovers personal data, connects findings to lineage and ownership context, and helps maintain Article 30 records.
A G2 reviewer reported integrating OvalEdge helped in reducing the share of their workday spent searching for data from 70% to 5%.
How it discovers and maps personal data
OvalEdge scans cloud warehouses, on-premises databases, and file systems for personal and Article 9 special-category data, with findings feeding directly into Data Lineage to show where information originates, how it moves, and which downstream systems hold copies.
Pre-built connectors read source metadata natively, and classifiers are tunable so privacy teams can detect industry-specific patterns without engineering support. Every match writes back into the Data Catalog with its lineage graph, keeping discovery output and audit trail as one object.
How it supports GDPR workflows
Three workflows operate within the same data catalog:
-
Article 30 records: Discovery and lineage changes keep processing records current.
-
DSAR fulfillment: Governed queries locate data associated with an individual across connected systems.
-
Right to erasure: Data Access Governance and lineage help teams identify downstream copies and track deletion.
All three draw from governed data assets rather than parallel spreadsheets, so an Article 30 review pulls from the same live inventory that answers a DSAR. Approvals, ownership, and change history run through the stewardship layer, giving auditors a single evidence trail. The graph also traces personal data used for AI training and automated decision-making, connecting evidence directly to underlying assets.
Pricing is license-based, scaling with what you connect and who curates rather than with data volume.
Hallmark uses OvalEdge to run Right to Know and Right to Delete requests through a single catalog, combining PII classification, business glossary, and governed queries into one privacy workflow. The result: consistent visibility into where consumer PII lives, routed requests with ownership and audit trails, and a foundation that now extends into data quality and AI-ready analytics.Read the Hallmark case study.
Where it fits and falls short
-
Where it fits: Best for regulated enterprises that need strong lineage, privacy workflows, and flexible deployment.
-
Where it falls short: Setup may take longer than with lightweight privacy tools because teams must configure connectors and adopt the catalog as a governance source. Reviews also report difficulty finding PII in unstructured data.
A 2026 Forrester TEI study of a composite OvalEdge customer found 337% ROI with payback in under six months, a 75% reduction in compliance team effort for sensitive data discovery, and PII/PCI detection across an enterprise in 45 days from proof-of-concept start.
See what OvalEdge can do with your data. Book a demo today and test it against a real DSAR, Article 30 review, or erasure request from your own environment.
2. BigID
Best for: Large enterprises with hundreds of databases, data lakes, and cloud sources.
BigID is an enterprise data intelligence platform for organizations with large data estates and mature privacy programs. It uses machine learning to discover, correlate, and classify personal data across structured, unstructured, cloud, and SaaS sources.
How it discovers and maps personal data
BigID continuously scans databases, files, cloud object stores, and SaaS applications. Its classifiers detect personal data and Article 9 special categories, while identity correlation connects findings to individual data subjects.
How it supports GDPR workflows
Three GDPR workflows operate on the discovery layer:
-
Article 30 records: The data inventory updates processing records as new sources are connected.
-
DSAR fulfillment: Identity-correlated searches locate records associated with an individual and support collection and delivery.
-
Right to erasure: Deletion actions run across connected systems and create an audit trail.
BigID applies the same classification capabilities to personal data entering AI training and automated decision-making systems. Cloud and on-premise deployments are available, while pricing is quote-based.
Where it fits and falls short
-
Where it fits: Best for large enterprises with dedicated privacy teams and hundreds of sources to scan. Financial services, healthcare, and other regulated organizations benefit most from its classification depth and ability to process complex data estates.
-
Where it falls short: Deployment can take months, connector setup may require engineering support, and costs can be high for smaller teams. Reviews report slow issue resolution and identity correlation that needs frequent tuning. Lean teams may prefer a simpler SaaS-native privacy platform.
3. IBM Guardium
Best for: Regulated industries running mainframes, DB2, or legacy database estates.
IBM Guardium Data Protection combines sensitive data discovery with continuous database activity monitoring. It suits banks, insurers, and healthcare organizations that need GDPR compliance alongside visibility into who accesses regulated data.
How it discovers and monitors personal data
Guardium Discover and Classify scans structured databases, unstructured files, warehouses, and cloud stores. It identifies personal and Article 9 special-category data, while Guardium Data Protection monitors access, queries, and policy changes in real time.
How it supports GDPR workflows
Three workflows operate across the discovery and monitoring layers:
-
Article 30 records: Classification results support processing inventories, although full register management may require GRC tooling.
-
DSAR fulfillment: The data inventory supports searches across connected sources and integrates with external workflow tools.
-
Right to erasure: Database controls execute deletion, while Guardium records the access and deletion trail.
Personal data entering AI systems requires additional governance coverage from dedicated AI compliance software. Existing IBM customers can connect Guardium with watsonx.governance for AI oversight.
Where it fits and falls short
-
Where it fits: Best for regulated enterprises that need mainframe coverage, real-time database monitoring, and continuous compliance reporting across on-premise, cloud, and hybrid environments.
-
Where it falls short: Deployment and licensing can be demanding for privacy-first teams. Users say SIEM integration gaps and extensive customization requirements for incident metadata.
4. OneTrust
Best for: DPO-led privacy programs consolidating consent, DSAR, and Article 30 requirements in one suite.
OneTrust Privacy Automation helps privacy and legal teams manage GDPR obligations through one platform. It combines data discovery with consent management, DSAR automation, processing records, and privacy risk workflows.
How it discovers and maps personal data
OneTrust’s Data Use Governance capabilities scan databases, file systems, cloud stores, and SaaS applications. Findings feed the privacy platform, connecting discovered data with processing activities, consent records, and data-subject workflows.
How it supports GDPR workflows
Three workflows operate on the discovery layer:
-
Article 30 records: Privacy teams can create and maintain processing records without extensive engineering support.
-
DSAR fulfillment: Automated workflows cover intake, identity verification, data collection, review, deletion, and secure delivery.
-
Right to erasure: The workflow engine coordinates deletion across connected systems and maintains verification records.
Personal data used by AI systems is managed through the separate AI Governance solution. Buyers should include the additional module when evaluating coverage and pricing. Packages are quote-based and designed for enterprise privacy programs.
Where it fits and falls short
-
Where it fits: Best for DPO offices and legal teams that want consent, processing records, DSAR automation, and privacy risk management under one platform.
-
Where it falls short: Configuration can take weeks and may require implementation support. Customer feedback flags disruptive interface changes and heavy promotion of AI features.
5. Securiti
Best for: Privacy teams automating DSAR and erasure workflows across multi-cloud environments.
Securiti is a Data and AI security platform centered on privacy automation. It combines continuous personal data discovery, DSAR orchestration, consent management, and AI governance within one system.
How it discovers and maps personal data
Securiti scans cloud warehouses, on-premise databases, SaaS applications, and unstructured file stores. Its People Data Graph links discovered personal and Article 9 special-category data to individual data subjects, supporting automated privacy workflows.
How it supports GDPR workflows
Three workflows operate on the discovery layer:
-
Article 30 records: Live discovery data updates processing purposes, lawful bases, and transfer details.
-
DSAR fulfillment: Automated workflows handle identity checks, data collection, redaction, and delivery.
-
Right to erasure: Deletion runs across connected sources with verification and audit evidence.
Securiti also applies its classifiers to data entering AI training and LLM pipelines. Its AI governance capabilities monitor training data, prompt risks, and regulatory obligations. Pricing is quote-based and designed for mid-market and enterprise buyers.
Where it fits and falls short
-
Where it fits: Best for privacy teams that need multi-cloud discovery, fast DSAR automation, and AI governance within one platform. No-code workflows also reduce engineering dependence.
-
Where it falls short: Classifier tuning can slow onboarding, with user feedback citing a setup period of about three weeks. Enterprise pricing may also exclude smaller teams.
6. MineOS
Best for: Mid-market privacy teams managing SaaS sprawl, consent, and AI asset discovery.
MineOS is a cloud-native privacy and AI governance platform designed for fast deployment. It combines personal data discovery, DSAR automation, consent management, and AI asset inventory within one interface.
How it discovers and maps personal data
MineOS scans SaaS applications, cloud warehouses, and structured databases for personal and Article 9 special-category data. Its shadow IT discovery capabilities identify unsanctioned tools and add findings to a live personal data inventory.
How it supports GDPR workflows
Three workflows operate on the discovery layer:
-
Article 30 records: Live inventory data updates processing purposes and lawful bases.
-
DSAR fulfillment: No-code workflows automate intake, identity verification, data collection, and delivery.
-
Right to erasure: Native integrations execute deletion and record confirmation across connected systems.
MineOS also discovers shadow AI tools and maintains an inventory of AI systems, owners, purposes, and associated data. Pricing targets mid-market teams, while deployment is cloud-based.
Where it fits and falls short
-
Where it fits: Best for mid-market privacy teams that need fast SaaS discovery, automated DSR workflows, and shadow AI visibility without dedicated privacy engineers.
-
Where it falls short: Legacy database and unstructured-data coverage may not match enterprise tools. Customer feedback also flags occasional bugs and limited multi-brand, multilingual templates.
7. Strac
Best for: SaaS-heavy stacks needing real-time DLP, browser-level redaction, and rapid GDPR remediation.
Strac is a cloud-native data security platform centered on real-time detection and remediation. It combines DSPM, DLP, and browser controls to identify and remove sensitive data while employees use SaaS and AI tools.
How it discovers and protects personal data
Strac scans SaaS applications, cloud storage, endpoints, and browser activity for personal and Article 9 special-category data. Its SaaS DLP capabilities redact sensitive information from Slack, Zendesk, Google Drive, and other collaboration tools in real time.
How it supports GDPR workflows
Three workflows operate on the real-time discovery layer:
-
Article 30 records: SaaS inventory supports processing records but may require a separate privacy suite for full management.
-
DSAR fulfillment: Searchable inventories locate personal data across connected SaaS sources.
-
Right to erasure: Automated redaction or removal occurs within the source system, with each action logged.
Strac can also detect personal data entered into AI assistants and block or redact it before submission. Deployment is cloud-native and supports browsers, SaaS platforms, endpoints, and cloud systems. Pricing is scoped by protected surfaces, integrations, data volume, and employee count.
Where it fits and falls short
-
Where it fits: Best for SaaS-heavy companies that need fast PII detection, real-time redaction, and browser controls across collaboration and customer-support tools.
-
Where it falls short: Database and on-premise coverage may not match enterprise platforms. User feedback also calls for continued ML model improvements, while Strac does not replace a full privacy workflow suite.
8. Varonis
Best for: Teams managing unstructured data governance across file shares, SharePoint, and collaboration tools.
Varonis Data Security Platform combines sensitive data discovery, permissions analysis, and threat detection. It suits organizations where personal data risk is concentrated in files, Microsoft 365, SharePoint, and other collaboration platforms.
How it discovers and protects personal data
Varonis discovers and classifies personal and Article 9 special-category data across file shares, Microsoft 365, Salesforce, Box, Google Workspace, and databases. Permission analysis shows who can access sensitive data, who uses it, and where files are overexposed.
How it supports GDPR workflows
Three workflows operate on the discovery and permissions layer:
-
Article 30 records: Data inventories support processing records but usually require a dedicated privacy suite for full management.
-
DSAR fulfillment: Search tools locate subject data across file repositories for export into external workflows.
-
Right to erasure: File-level deletion and permission changes create access and remediation trails.
Varonis also monitors unusual access to sensitive data through its MDDR service. Pricing is enterprise-custom, with SaaS and on-premise coverage available for different environments.
Where it fits and falls short
-
Where it fits: Best for security teams that need deep file visibility, permissions governance, insider-risk detection, and GDPR discovery across Microsoft-heavy or hybrid environments.
-
Where it falls short: Varonis does not replace full DSAR or consent management software, and costs can be high. Customer feedback also requests more flexible dashboard customization.
9. Microsoft Purview
Best for: Microsoft-native organizations running Microsoft 365, Azure, and Copilot at scale.
Microsoft Purview combines data discovery, classification, information protection, DLP, governance, and compliance. It suits organizations that want native controls across Teams, SharePoint, OneDrive, Azure, Fabric, and Copilot.
How it discovers and maps personal data
Purview scans Microsoft and third-party data sources for personal and Article 9 special-category data. Its data governance capabilities create a searchable inventory, while sensitivity labels and protection policies follow data across supported Microsoft services.
How it supports GDPR workflows
Three workflows operate on the discovery layer:
-
Article 30 records: Classification and compliance templates help map processing activities to GDPR controls.
-
DSAR fulfillment: eDiscovery tools search Microsoft 365 workloads and package results for review and export.
-
Right to erasure: Retention, disposition, and deletion policies remove data while preserving audit records.
Purview also extends data security and compliance controls to Microsoft 365 Copilot and other AI applications. Pricing options include Microsoft 365 E5, Purview Suite, and pay-as-you-go plans.
Where it fits and falls short
-
Where it fits: Best for Microsoft-focused enterprises that need unified classification, DLP, eDiscovery, and Copilot protection across Microsoft 365, Azure, and hybrid environments.
-
Where it falls short: Diverse estates and cross-tenant deployments can require specialist expertise. User feedback also identifies initial setup and pricing as potential concerns.
Why GDPR data discovery software is critical for compliance
GDPR does not require discovery software. However, the official GDPR regulation text creates documentation, data-subject rights, impact assessment, and breach-reporting obligations that become harder to manage across changing data estates.
1. Article 30 records and DPIA evidence
Article 30 generally requires organizations to document processing purposes, data categories, recipients, international transfers, retention periods, and security measures. Article 35 also requires a Data Protection Impact Assessment before processing likely to create a high risk to individual rights and freedoms.
Discovery software keeps the supporting inventory current as teams:
-
Adopt new SaaS applications.
-
Add datasets and processing activities.
-
Create vendor and cross-border data flows.
Data lineage compliance software gives privacy teams stronger evidence by connecting inventory changes to their sources and downstream processing.
To keep Article 30 records reliable, make inventory updates part of change management. Require every new system, pipeline, or data flow to have an owner and classification before launch, so documentation changes alongside the data estate instead of during an annual cleanup.
2. DSAR fulfillment and erasure
Requests can cover access, correction, portability, and erasure. Organizations normally have one month to respond, with a two-month extension permitted for complex or numerous requests.
An EDPB access request review identified seven implementation challenges. Missing documented procedures was one, while request volume and organization size also affected compliance.
Discovery software helps teams locate records across connected systems, document downstream deletion, and track valid retention exceptions without relying on ad hoc searches.
3. Faster breach scoping
Article 33 requires organizations to notify the relevant supervisory authority within 72 hours where feasible, unless the breach is unlikely to risk individual rights and freedoms.
Teams must quickly establish:
-
Which systems were affected.
-
What personal data they contained.
-
Which data subjects may be involved.
A current discovery inventory turns breach scoping into a structured search, helping legal and security teams prepare a more accurate notification within the statutory window.
How to choose the right GDPR data discovery software
Start by defining what the platform must cover. Then test each shortlisted tool against the same requirements using your own data.
Before evaluation, confirm:
-
Regulatory scope: Identify every regulation the platform must support.
-
Data coverage: Map the systems containing personal data.
-
Platform ownership: Assign the team responsible for implementation and management.
For a mixed data estate, separate discovery from classification. First map data locations, ownership, and access history across every service. Then configure classification and DLP policies against the verified inventory.
Use the same evaluation matrix for every platform:
|
Evaluation area |
What to check |
POC test |
|
Discovery |
Can the platform accurately classify personal data across your systems? |
Scan a labeled sample and measure the results. |
|
Data mapping |
Does the inventory update automatically when data changes? |
Add a source and review the updated map. |
|
Privacy workflows |
Can the platform complete GDPR requests without manual handoffs? |
Run a mock DSAR from intake to response. |
|
Deployment |
Does the platform meet your infrastructure and residency requirements? |
Test deployment controls in your intended environment. |
Choose the platform that fits your GDPR needs
A lean privacy team has different needs from a regulated enterprise managing hybrid infrastructure. Match the platform to your GDPR scope and operating model. Then test it against a real DSAR or erasure request before committing.
For organizations connecting privacy to broader data governance, OvalEdge keeps discovery, cataloging, and lineage within one platform. Article 30 records stay connected to the current data estate, while privacy actions retain traceable evidence for audits.
If that model fits your organization, book a demo with OvalEdge and test it against a sample of your own data.